95% of breaches
are caused by
people.
Not technology. Not systems failures. People.
That's the finding from a decade of OAIC breach reports — and it's why Dr. James Carlopio built a risk assessment that looks at the human element, not just the tech stack.Dr. James Carlopio built an assessment that measures the human risk — not just the tech.
Dr. James Carlopio, Ph.D.
Organisational Psychologist & Cyber Security Expert
University of Queensland
95%
of breaches: human causes
OAIC Data, 2018–2026
The Office of the Australian Information Commissioner has tracked breach causes for nearly a decade.
95%
of breaches caused by people
The Implication
Yet cyber security spending on people and education is just 5% of tech-related spending.
5%
About the Creator
Dr. James Carlopio, Ph.D.
Organisational Psychologist. Cyber Security Researcher. 30+ Years.
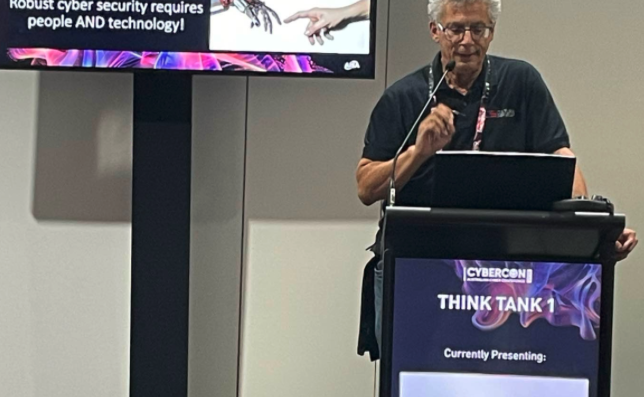
CyberCon — Think Tank 1
"Robust cyber security requires people AND technology"
35+
Peer-reviewed publications
5
Books on socio-technical systems
30+
Years of industry consulting
PhD
Organisational Psychology, UQ
"People have been trying to solve cyber security with technology forever. They're solving a human problem with technology — when the problem is the humans."
— Dr. James Carlopio
James holds a doctorate in Organisational Psychology and teaches at the University of Queensland in the Master of Cyber Security program. He has spent over three decades at the intersection of human behaviour and organisational systems — including how people create, and can prevent, cyber security incidents.
He has consulted to some of the world's most complex organisations, including the United Nations, IBM, ANZ Bank, Commonwealth Bank, Telstra, Optus, and the Australian Federal Police — advising on the human factors that determine whether technical changes, and security investments, succeed or fail.
James has published over 35 peer-reviewed articles and 5 books on socio-technical systems — the study of how people and technology interact. His research consistently arrives at the same conclusion the OAIC data has confirmed since 2018: the overwhelming majority of breaches trace back to human behaviour, not technical failure.
He has presented at cyber security conferences around the world — including AUSCERT, CyberCon, AISA and ROCON — making the case that organisations cannot buy their way out of a people problem. The Cyber Risk Assessment is the practical tool that puts his methodology within reach of any business.
Has consulted to
The Difference
Most tools measure
your tech.
This one measures
your exposure.
Attacker's perspective
We don't audit your firewall. We calculate how attractive your business looks to a cybercriminal — based on your industry, your data, and your human behaviours.
FAIR methodology
Factor Analysis of Information Risk is the leading open standard for quantitative risk. Not a checklist — a rigorous, repeatable calculation.
Customised to your business
A healthcare practice faces completely different risks than a retail shop. The assessment accounts for your industry, your data type, and your specific exposure.
Vendor independent
James has no products to sell you. This is an honest, unbiased risk estimate — so you can make informed decisions about where to invest.

Process
Three steps. Five minutes.
Answer 22 questions
Plain-English questions about your industry, your data, and your people. No IT knowledge required.
We calculate your score
Dr. Carlopio's assessment calculates your likelihood of a breach and the likely magnitude of its impact based on the Factor Analysis of Information Risk model, open sourced and proprietary data, and the information you provide.
Get your report instantly
A professionally formatted PDF with your score, risk band, and personalised priority recommendations.
"Our staff, their children, parents and grandparents are getting scammed at alarming rates. We simply do not have the cyber security skills we need to stay safe online. Every school needs to add cyber security to the curriculum."
Dr. James Carlopio, Ph.D.
University of Queensland
